
A hijacked TensorLake npm release used a preinstall hook to steal credentials, run remote commands, and potentially expose data through GitHub.
Recommended
 AI Noise Is the New Development BottleneckSonatype
Limits of Java Certificate Bypass: Fingerprint Blocklist InsightsSonatype
The New Release Metric: Less Cleanup Per ReleaseSonatype
Q3 2026 Open Source Malware Index: When Compromise CompoundsSonatype
Shadow AI Across Government: It's Three Problems, Not OneSonatype
eMudhra CA Incident: Sonatype's Assessment and GuidanceSonatype
 Pulumi ESC Table Editor Now Supports Dynamic Credential and Secret IntegrationsPulumi
 How We Eliminated Long-Lived CI Secrets Across 70+ ReposPulumi
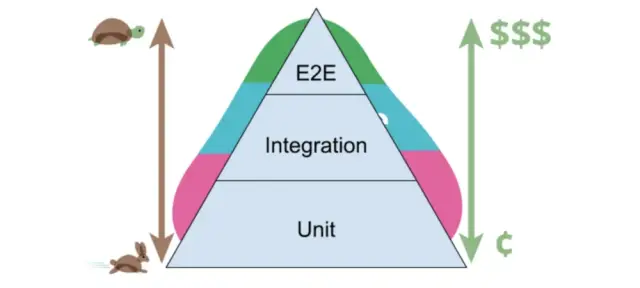 Develop, Preview, TestCss Tricks
 Install the Collector on macOSOpentelemetry
 How Basecamp Uses Basecamp 3 to Manage Team Projects and Simplify CommunicationZapier
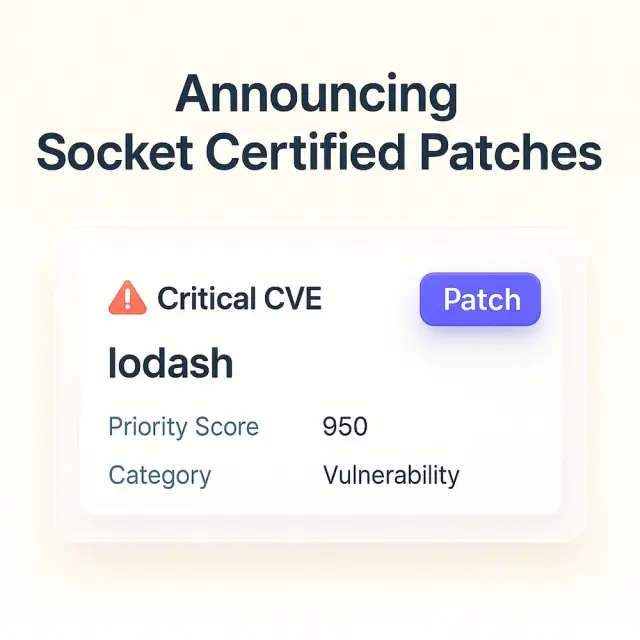 Announcing Socket Certified Patches: One-Click Fixes for Vulnerable DependenciesSocket
 Introducing Dependency Divergence GitHub ActionSocket
 Updated and Ongoing Supply Chain Attack Targets CrowdStrike npm PackagesSocket
 upm Launches as a Fast, Tiny Package Manager Written in TypeScriptSocket
 Happy Birthday, Shai-HuludSocket
 GlassWorm Loader Hits Open VSX via Developer Account CompromiseSocket
 Forward Compatibility and Toolchain Management in Go 1.21 - The Go Programming LanguageGo
 Webinar: Migrate from Legacy Platforms to Datadog with AeginDatadoghq
Install the Collector with DockerOpentelemetry
