
Action required: Upgrade Windows clients to v1.32.3
Tailscale has recently been notified of security vulnerabilities in the Tailscale Windows client which allow a malicious website visited by a device running Tailscale to change the Tailscale daemon configuration and access information in the Tailscale local and peer APIs.
 How Instacart reduces developer disruptionsTailscale
Finaloop improves connectivity and eliminates complaints with TailscaleTailscale
How Krumware saves time and reduces costs on Kubernetes with TailscaleTailscale
Why Corelight severed ties with their old VPNTailscale
How Dexory secures a global fleet of inventory robots with TailscaleTailscale
Vanta upgrades to modern, frictionless networking with TailscaleTailscale
 Digital Forensics & Emerging Technologies GuideCybersecurity Exchange
 How a marketing agency increased client conversions 35% with Zapier CanvasZapier
 Looping by Zapier: Repeat actions for itemsZapier
 System UIconsCss Tricks
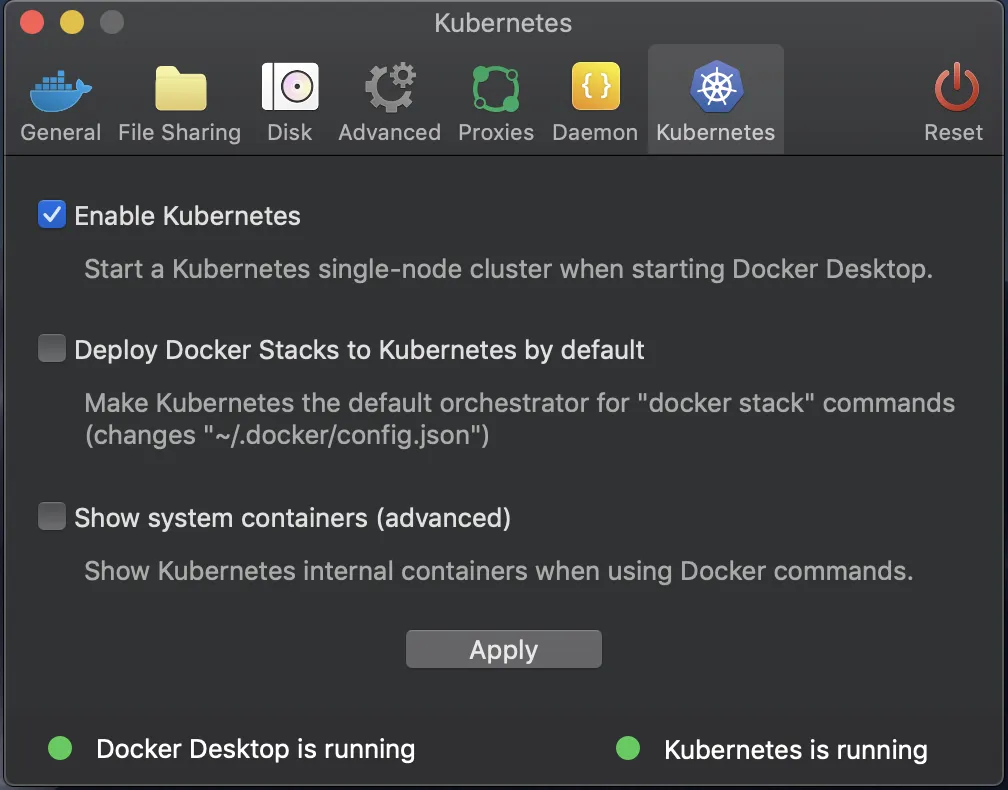 Depend on Docker for KubeflowDocker
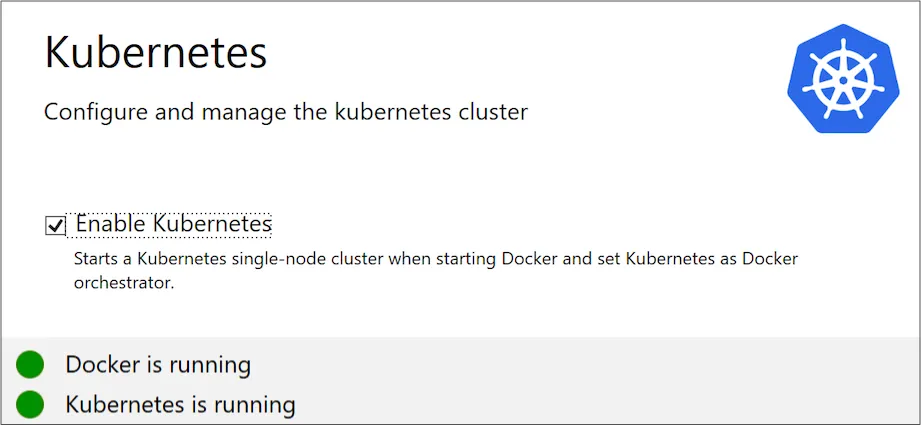 Docker for Windows Desktop with KubernetesDocker
 Credit pricing - MintlifyMintlify
 .NET Framework instrumentation configurationOpentelemetry
 How to connect Firebase to a Google SheetZapier
 Zapier Tables: Take action on your data automaticallyZapier
 How to automatically add new Microsoft Dynamics contacts to MailchimpZapier
 Introducing Dependency Divergence GitHub ActionSocket
 Siloscape: Windows Malware That Breaks KubernetesThenewstack
 React Authentication & Access ControlCss Tricks
