
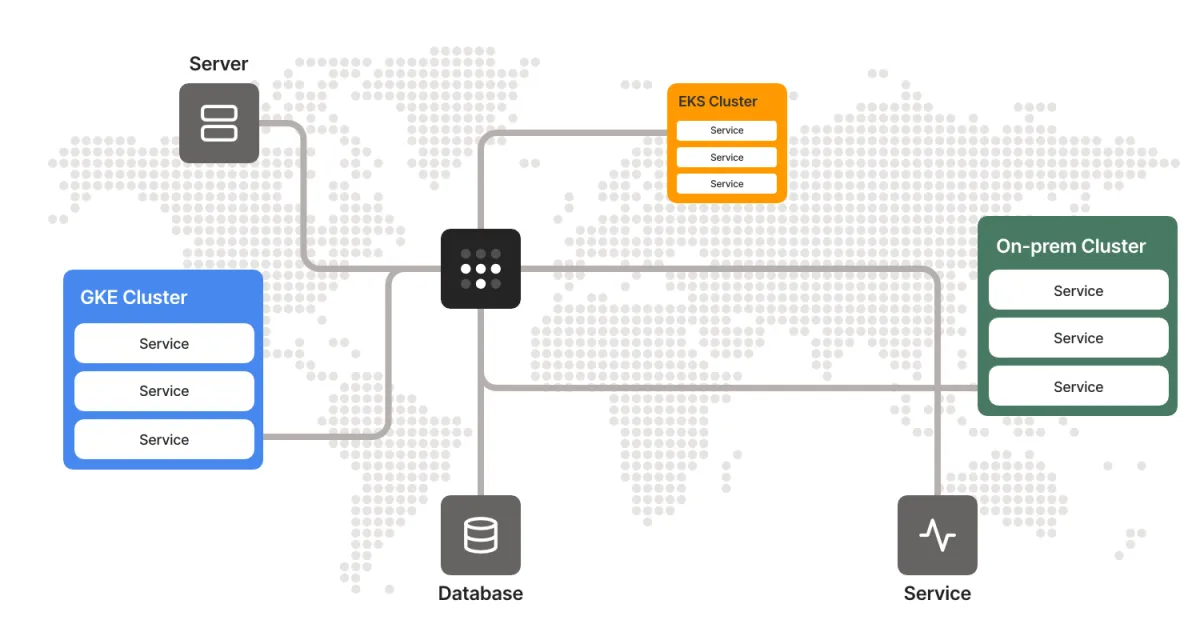
Tailscale Kubernetes Operator generally available for simple, secure K8s access
Secure Kubernetes control plane access and record kubectl exec commands with Tailscale’s Operator—no public exposure or complex VPNs required.
 How Krumware saves time and reduces costs on Kubernetes with TailscaleTailscale
How Awesome improved access and user management by 90% with TailscaleTailscale
How Cloudfleet builds a better Kubernetes with TailscaleTailscale
How Firetiger built secure agent-to-database connectivity with TailscaleTailscale
How Instacart reduces developer disruptionsTailscale
Finaloop improves connectivity and eliminates complaints with TailscaleTailscale
 Local Kubernetes Development Using Minikube and Redis EnterpriseRedis
 How CoverDoc uses AI to revolutionize cover letter writingZapier
 How Argo CD and OpenShift Enable GitOps for DevelopersThenewstack
 Google Anthos from the Eyes of a Kubernetes DeveloperThenewstack
 Security Considerations for API-Driven Apps Deployed to CloudThenewstack
 Oso Unbundles Security AuthorizationThenewstack
 Pulumi ESC and External Secrets Operator: The Perfect Solution for TodayPulumi
 AWS Enterprise Container Management with PulumiPulumi
 IaC Best Practices: Implementing RBAC and SecurityPulumi
 New Policy as Code Capabilities with CrossGuardPulumi
 Supporting Kubernetes with Faster, Easier Test EnvironmentsPulumi
 Neo Integrations: MCP Servers and Cloud CLIsPulumi
 Introducing: H100s on ModalModal
 The Serverless Backend for Analytics: Introducing MotherDuck’s Native Integration on VercelMotherduck
