This bank data stealing Android malware is back - and it's now even sneakier
BankBot trojan malware waits twenty minutes after the app is used before moving to run its payload.

 FBI says credential stuffing attacks are behind some recent bank hackszdnet.com
 Oracle Cloud Guard, Maximum Security Zones now availablezdnet.com
 Zerologon attack lets hackers take over enterprise networks: Patch nowzdnet.com
The pandemic strikes tech: What will recovery look like?zdnet.com
 Google sets virtual Pixel, Chromecast event for Sept. 30zdnet.com
 Verizon acquires Tracfone in $6.25 billion dealzdnet.com
We’ve Hit the AI Inflection Point. Now What?BrightTALK
Investing in the AI Value Chain: From Chips to Power, Data and ConnectivityBrightTALK
Odyssey: The Seven Monsters of PAMBrightTALK
The Identity Blind Spot: Why AI Agents Are the Access Control Gap…BrightTALK
Endpoint Security ReimaginedBrightTALK
AI-Driven Data Analytics and Decision Intelligence Summit 2026…BrightTALK Summits
Are We There Yet? A Digital Maturity Model for Enabling Process…BrightTALK
AI-Ready IT Starts with CMDB Reality: The Data Foundation for…BrightTALK
DeepL on AWS Marketplace | Enterprise translation, deployed fastdeepl.com
Secure Language AI solutions for global business | DeepLdeepl.com
DeepL Voice now preserves your voice in real time across languagesdeepl.com
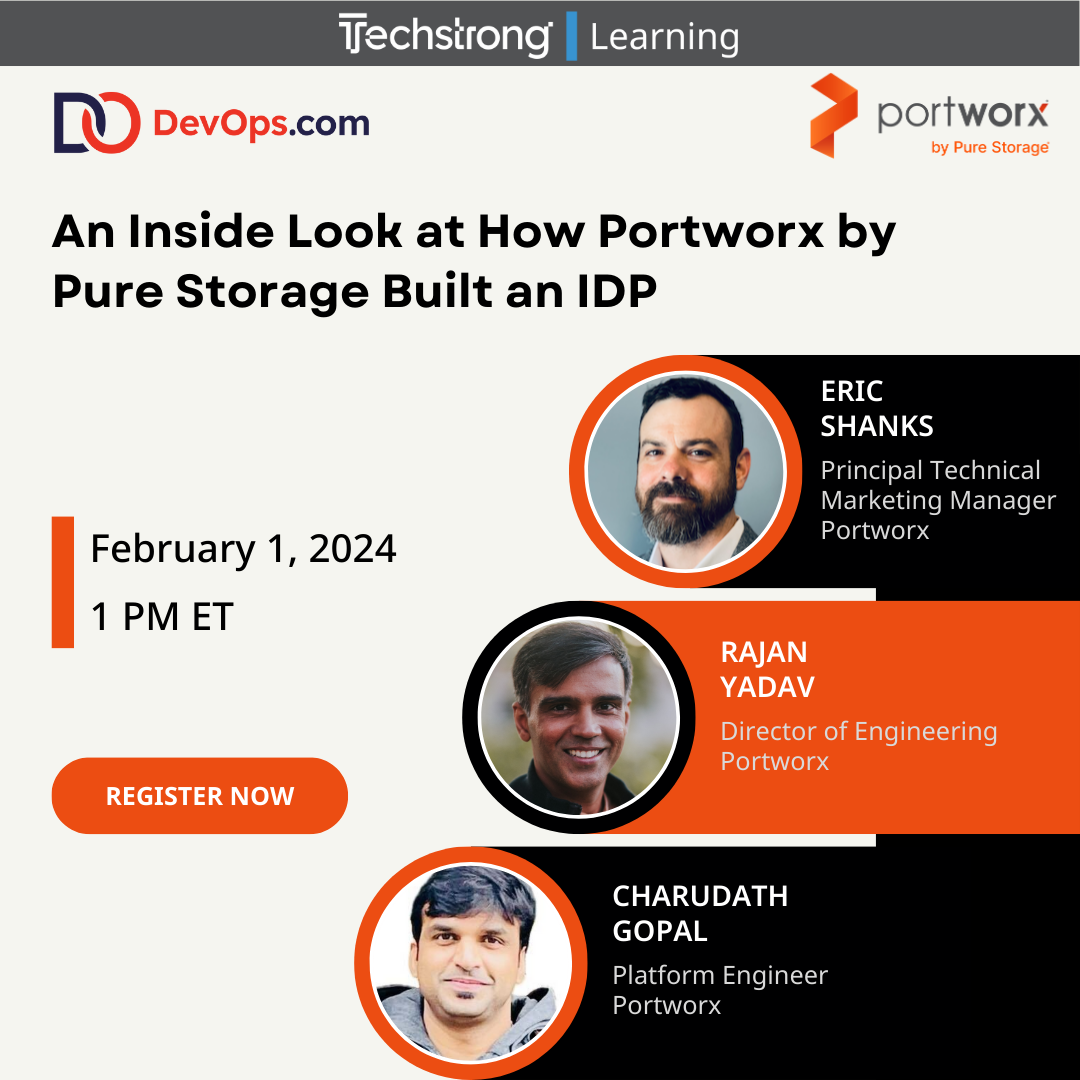 An Inside Look at How Portworx by Pure Storage Built an IDPwebinars.devops.com
 Vroom, vroom.theverge.com
 Sonos speakers and soundbars are 25 percent off for existing customerstheverge.com