
Vulnerability Scanning Process - Aqua
Learn how vulnerability scanning works & discover 4 stages of the vulnerability scanning process: identification, scoring, remediation & reporting.
 Cloud Workload Security: Aqua Shines in GigaOm's Radar ReportAquasec
 Aqua and HashiCorp Enable Cloud Native Security, Zero-Trust ApproachesAquasec
 Sink or Swim: Tackling 2024's Record-Breaking Vulnerability WaveAquasec
 Looney Tunables Vulnerability Exploited by KinsingAquasec
 Cloud VM Security with Aqua CSPAquasec
 Vulnerability Management in Container ImagesAquasec
 How we grew Mintlify by doing things that don't scaleMintlify
 Read Every Single ErrorPulumi
 container_processModal
 ArchitectureOpentelemetry
 Webinar Recap: Webinar Recap: Securing the Software Supply Chain with Docker BusinessDocker
 Protecting Secrets with DockerDocker
 Vercel QueuesVercel
 Reporting directive - GlossaryDeveloper Mozilla
 Questions to Ask Your Hardened Image ProviderDocker
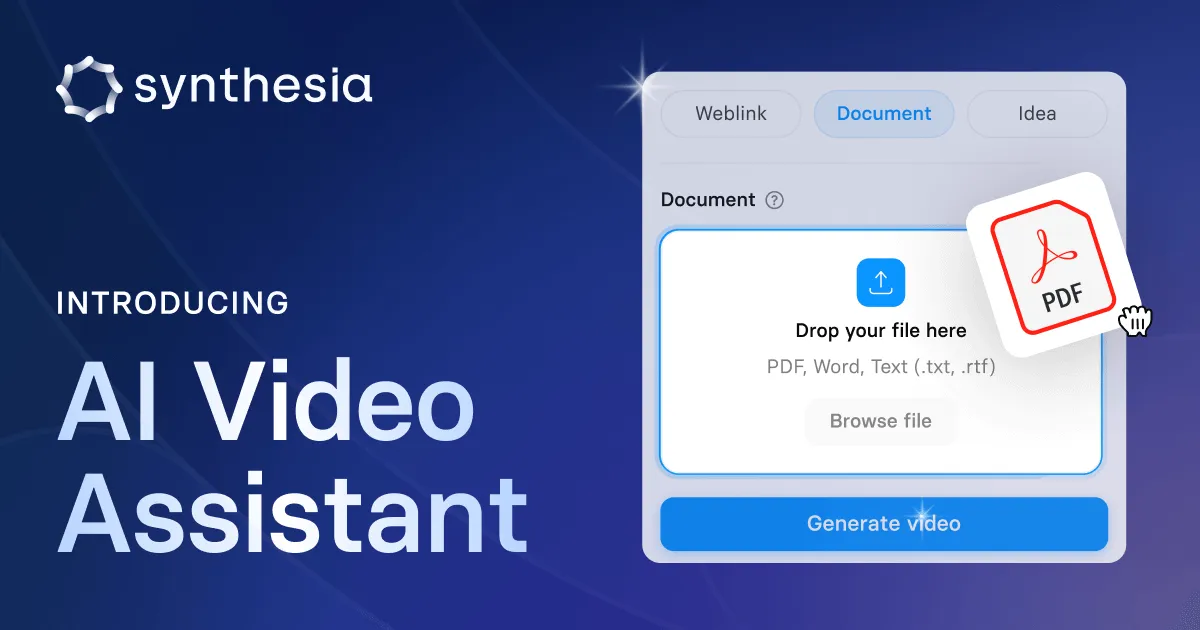 Introducing AI Video Assistant, a new way to turn text into engaging videosSynthesia
 Vulnerability Scanning is BrokenSocket
 Unpacking the ROI of Coana's SCA With Reachability AnalysisSocket
 Socket Now Protects the Firefox Extension EcosystemSocket
 Socket Joins New OpenJS Program to Fund Node.js Security WorkSocket
