
Aqua News New Timing Attack Against NPM Registry API Could Expose Private Packages
"By creating a list of possible package names, threat actors can detect organizations' scoped private packages and then masquerade public packages, tricking employees and users into downloading them," Aqua Security researcher Yakir Kadkoda said.
 Threat Alert: Private npm Packages Disclosed via Timing AttacksAquasec
 Deceptive Deprecation: The Truth About npm Deprecated PackagesAquasec
 New npm Flaws Let Attackers Better Target Packages for Account TakeoverAquasec
Threat Alert: TeamTNT Pwn Campaign Against Docker and K8s EnvironmentsAquasec
 Cloud Workload Security: Aqua Shines in GigaOm's Radar ReportAquasec
 Aqua and HashiCorp Enable Cloud Native Security, Zero-Trust ApproachesAquasec
 Docs-as-code solutions for API teams: how to choose the right platform in 2026Mintlify
 Who Explains the Most? An Analysis of Educational YouTubers - Deepgram Blog ⚡️Deepgram
 Redis Cloud PrivateRedis
 OData or GraphQL? The Best Tech for Developing an API Is Neither or Both!Thenewstack
 Security Considerations for API-Driven Apps Deployed to CloudThenewstack
 How We Eliminated Long-Lived CI Secrets Across 70+ ReposPulumi
 Godoc: documenting Go code - The Go Programming LanguageGo
Go.dev: a new hub for Go developers - The Go Programming LanguageGo
 Managing dependencies - The Go Programming LanguageGo
 Modal SDKs for JavaScript and Go (alpha)Modal
 CSS Hell | CSS-TricksCss Tricks
 Real-Time Computational Physics with Wafer-Scale Processing [updated]Cerebras
 How to Use Your Own RegistryDocker
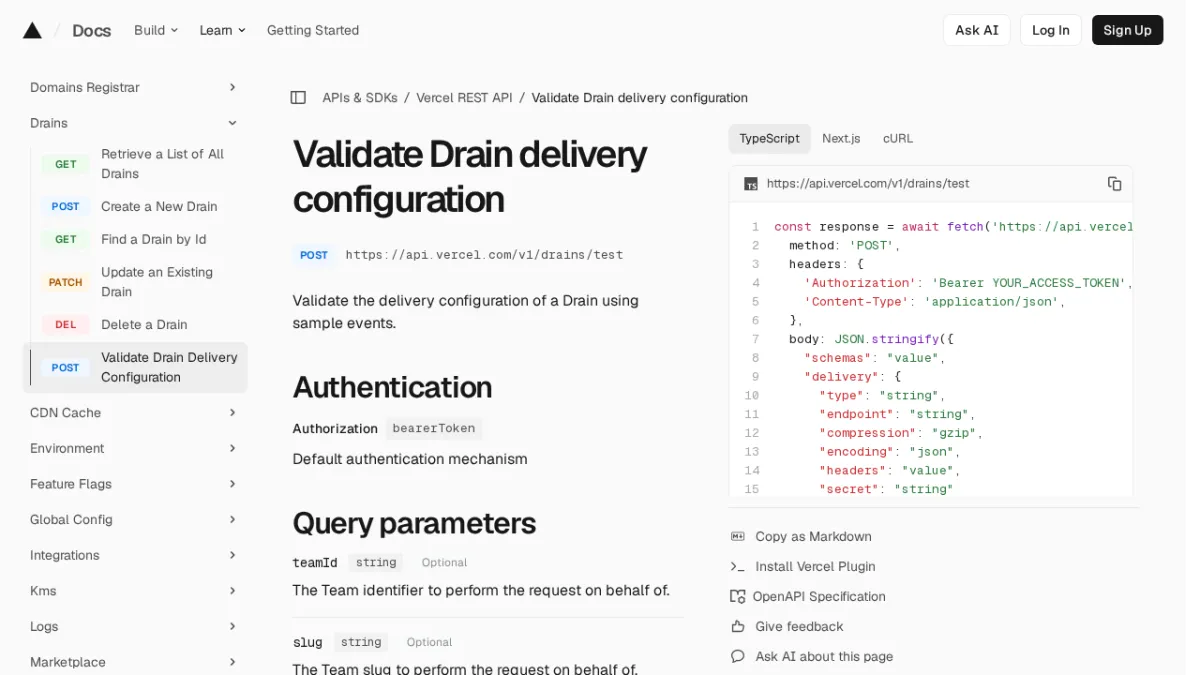 Validate Drain delivery configuration | Vercel REST APIVercel
