
Malware piggybacks on Windows' Background Intelligent Transfer Service
When Windows Update downloads patches to a PC, it relies on a service called the Background Intelligent Transfer Service, or BITS.
 Re: April 23rd AWS EU-WEST-1 Service InterruptionRedis
 7 ways to use Zapier's Zendesk integrationZapier
 Grafana Is Not Worried About AWS CommercializationThenewstack
 Cloud Systems: Deploying to Amazon ECSPulumi
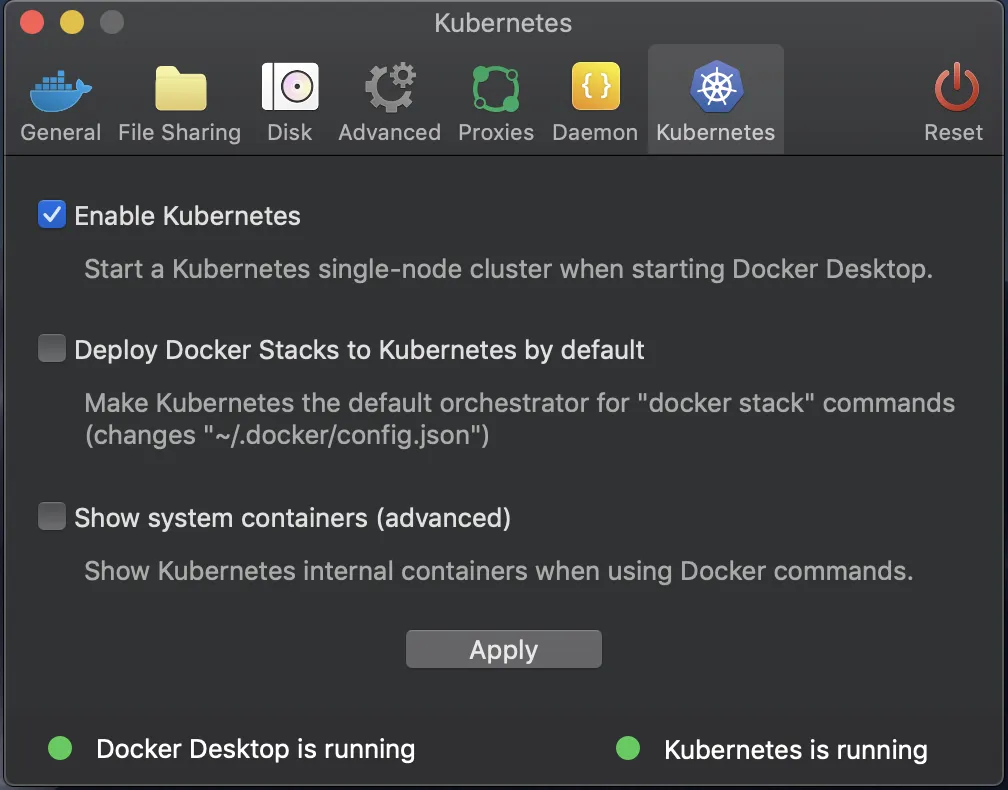 Depend on Docker for KubeflowDocker
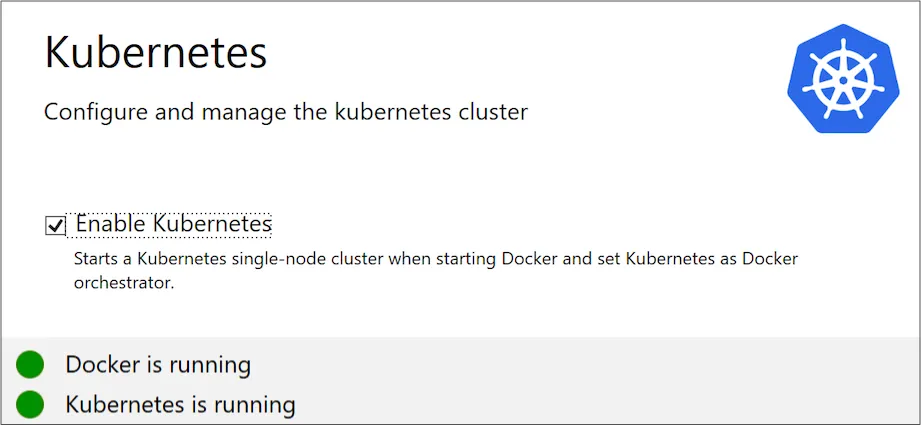 Docker for Windows Desktop with KubernetesDocker
 .NET Framework instrumentation configurationOpentelemetry
Instrumentation configurationOpentelemetry
 Anthropic Identifies Biased Reasoning and Recklessness as Drivers of Claude’s PyPI AttackSocket
 Twitch Browser Extension Exposes 30,000 Users’ OAuth Tokens to Russian Bot ServiceSocket
 Siloscape: Windows Malware That Breaks KubernetesThenewstack
 Improve Developer Experience: Increase Dev Productivity with Internal Developer PlatformsPulumi
 re:Invent 2020 EKS Feature ReleasesPulumi
 Netlify Background FunctionsCss Tricks
