
KeyDrift is a custom malware framework that UAT-11473 deployed after exploiting CVE-2026-20127, an authentication bypass in Cisco SD-WAN Catalyst Controller instances.
Recommended
 Goodfire says its new ‘inside-out’ monitors catch rogue AI agents at a fraction of the costTechcrunch
 Facebook hosted over 70 cybercrime groups that advertised all types of illicit activitycyberscoop.com
 Microsoft Edge, Internet Explorer zero-days could allow spying on your browsing activitycyberscoop.com
 How sloppy OPSEC gave researchers an inside look at the exploit industrycyberscoop.com
 Inside a Chinese hacking group's very flexible playbookcyberscoop.com
 Inside the online fight among DerbyCon leaders, illmob, and harassed infosec womencyberscoop.com
 The Most Important Work in AI Training Is Also the Most Overlooked - Deepgram Blog ⚡️Deepgram
 Redis Cloud PrivateRedis
 Inside the Go Playground - The Go Programming LanguageGo
 Position Sticky and Table HeadersCss Tricks
 4 ways to automate notifications for Mercado PagoZapier
 Defining “View Source”Css Tricks
 AI Needs Data, Data Needs AI: Inside the Data Outpost AgendaMotherduck
 Callback function - GlossaryDeveloper Mozilla
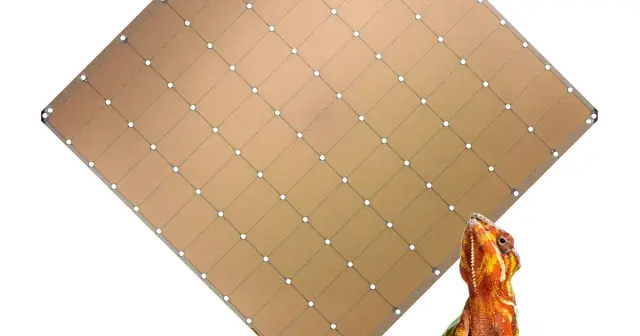 Cerebras Architecture Deep Dive: First Look Inside the HW/SW Co-Design for Deep Learning [Updated]Cerebras
 OpenTelemetry Tracing ShimOpentelemetry
 Socket Now Protects the Microsoft Edge Extension EcosystemSocket
 Conductor: Why We Migrated from Kubernetes to NomadThenewstack
 Inside Modal Notebooks: How we built a cloud GPU notebook that boots in secondsModal
 What is URL (Uniform Resource Identifier) and Percent Encoding?Bunny
