
WordPress patches a critical severity security vulnerability
The hole, which allows an unauthenticated attacker to perform remote code execution, is especially dangerous because many enterprises are not aware of all of their WordPress sites.
 Anthropic grants Project Glasswing access to 150 more companies, with a focus on criticalcsoonline.com
 Oracle's first monthly patch release fixes 35 flaws, including 11 rated 'critical'csoonline.com
 Microsoft says you don’t need another email security tool; experts say, not so fastcsoonline.com
 10 most critical LLM vulnerabilitiescsoonline.com
 Cloud Security at a Breaking Point: AI, Complexity, and the Future of Trustcsoonline.com
 Cybersecurity on the Front Lines of Critical Infrastructurecsoonline.com
 Cloud Security Trends & Challenges: Complete GuideCybersecurity Exchange
 Security Implementation for Responsible AI: A Practical FrameworkCybersecurity Exchange
 How to Conduct an AI Agent Security Audit [+ Checklist]Zapier
 How to connect Google Sheets to NotionZapier
 DevSecOps: Why Security Shouldn’t be Sacrificed for SpeedThenewstack
 Security Considerations for API-Driven Apps Deployed to CloudThenewstack
 Oso Unbundles Security AuthorizationThenewstack
 Pulumi ESC and External Secrets Operator: The Perfect Solution for TodayPulumi
 Announcing Restore Stacks: Recover Deleted Stacks in the Pulumi CloudPulumi
 IaC Best Practices: Implementing RBAC and SecurityPulumi
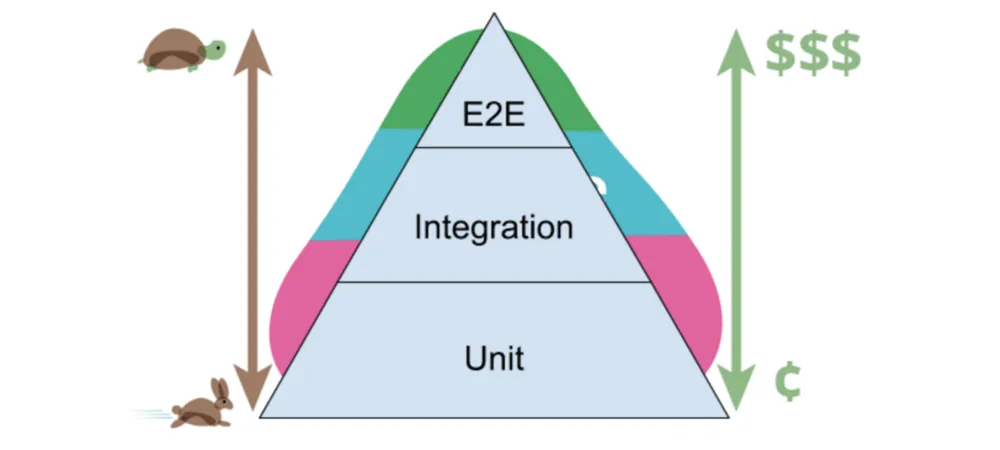 Develop, Preview, TestCss Tricks
 Jetpack Boost Handles Critical CSS For YouCss Tricks
 Docker at Cloud Expo Asia: GenAI, Security, and New InnovationsDocker
 Docker Networking Drivers - Details and Use CasesDocker
