
MacOS backdoor appears to be update of tool previously used by Vietnam-linked group APT32
Researchers at Trend Micro say a newly discovered MacOS backdoor uses tactics previously associated with the group known as APT32 or OceanLotus.
 China-based hackers used front companies to hack Uighurs, Facebook sayscyberscoop.com
 Finland implicates China-linked APT31 in parliament hackcyberscoop.com
 Researchers suggest Gorgon Group behind hacking spree that abused Bit.ly and Blogspotcyberscoop.com
 Top insurer CNA disconnects systems after cyberattackcyberscoop.com
 Federal advisories detail bitcoin payments to ransomware gangs, urgency of threatcyberscoop.com
 US racing to address Microsoft vulnerabilities, especially for small businessescyberscoop.com
 State of Speech: Our New Data Report Reveals ASR’s Untapped Potential - Deepgram Blog ⚡️Deepgram
 Automate Audio Transcription with Zapier + DeepgramDeepgram
 How Redis is Used in Practice | RedisRedis
Let’s Play Master and Servant: Real Time Synchronization Tool for Redis MigrationRedis
Redis OM .NET UpdateRedis
 Real Go Projects: SmartTwitter and web.go - The Go Programming LanguageGo
 Building an RL theorem-proving workflow on ModalModal
 Modal SDKs for JavaScript and Go (alpha)Modal
 Building a Remote MCP Server: OAuth, Tool Design & Lessons from 4,000+ AI Queries | MotherDuckMotherduck
 How to Use Google NotebookLM: The AI-Powered Research AssistantHeygen
 ESLINT_CONFIGURATIONVercel
 GraphQL setup - MintlifyMintlify
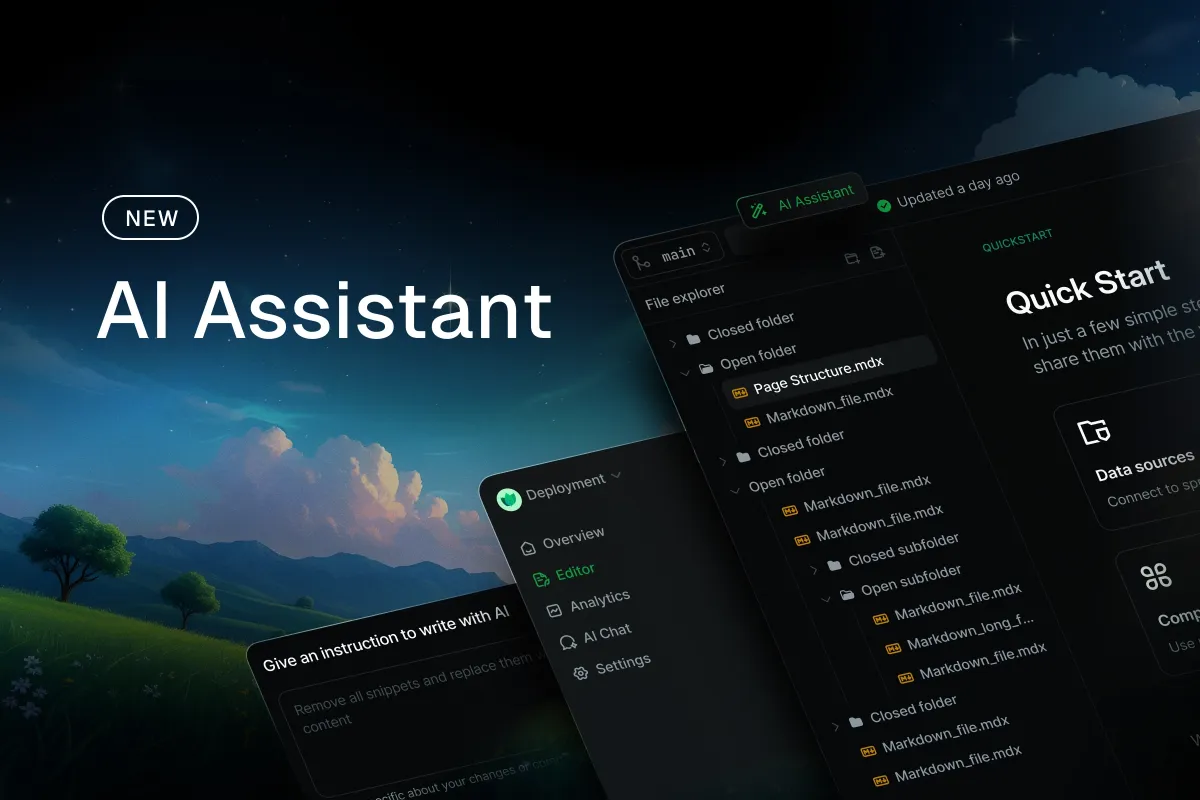 Introducing AI AssistantMintlify
 Detect Non-Inclusive Language with Retext and Node.js - Deepgram Blog ⚡️Deepgram
