
Responsible vulnerability disclosure is becoming an international norm
More and more democracies are adopting a policy of disclosing vulnerabilities as opposed sitting on them for their own intelligence gains.
 Top insurer CNA disconnects systems after cyberattackcyberscoop.com
 China-based hackers used front companies to hack Uighurs, Facebook sayscyberscoop.com
 Federal advisories detail bitcoin payments to ransomware gangs, urgency of threatcyberscoop.com
 US racing to address Microsoft vulnerabilities, especially for small businessescyberscoop.com
 Energy giant Shell impacted in Accellion hackcyberscoop.com
 Thousands of Exchange servers breached prior to patching, CISA boss sayscyberscoop.com
 Security Implementation for Responsible AI: A Practical FrameworkCybersecurity Exchange
 Launching a Framework for Responsible Practices for Synthetic MediaSynthesia
 Breakdown: The Kubernetes-Run AI Video Generation Pipeline for NIUS.TVThenewstack
 DuckDB, the great federator?Motherduck
 Web standards - GlossaryDeveloper Mozilla
 Webinar Recap: Webinar Recap: Securing the Software Supply Chain with Docker BusinessDocker
 Mental Health Marketing: A Responsible 2026 GuideHeygen
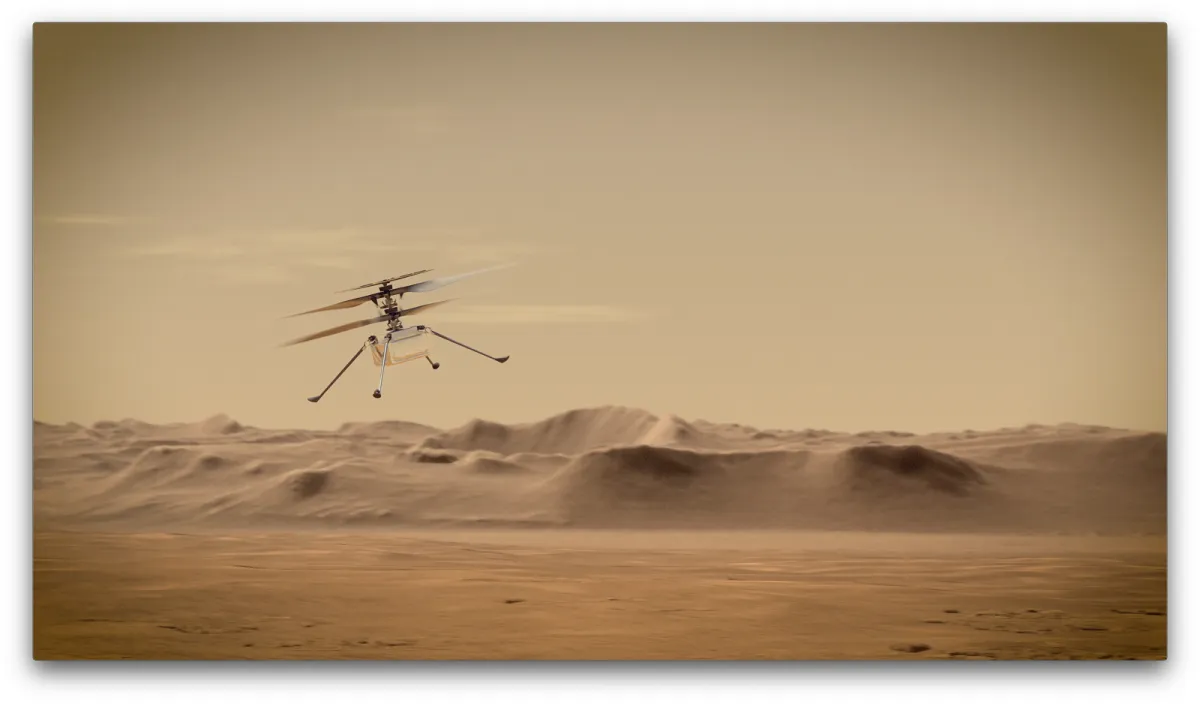 How the First Helicopter on Mars Uses Off-the-Shelf Hardware and LinuxThenewstack
 How to drive innovation in large organisationsSynthesia
 Vulnerability Scanning is BrokenSocket
 Unpacking the ROI of Coana's SCA With Reachability AnalysisSocket
 Socket Joins New OpenJS Program to Fund Node.js Security WorkSocket
 Next.js moves to scheduled security releasesSocket
 Sink or Swim: Tackling 2024's Record-Breaking Vulnerability WaveAquasec
