
What actually happens when a company examines third party risk
People in charge of information security at large U.S. companies spend the majority of their time assessing third party risk. How are they doing that?
 Top insurer CNA disconnects systems after cyberattackcyberscoop.com
 China-based hackers used front companies to hack Uighurs, Facebook sayscyberscoop.com
 Federal advisories detail bitcoin payments to ransomware gangs, urgency of threatcyberscoop.com
 US racing to address Microsoft vulnerabilities, especially for small businessescyberscoop.com
 Energy giant Shell impacted in Accellion hackcyberscoop.com
 Thousands of Exchange servers breached prior to patching, CISA boss sayscyberscoop.com
 Publish changes - MintlifyMintlify
 How we grew Mintlify by doing things that don't scaleMintlify
 Six Things to Consider When Using Redis on HerokuRedis
 Workato integrations: What's included and when to use ZapierZapier
 6 ways to use the Zapier Zoho CRM integrationZapier
 Get email alerts for Facebook Messenger messagesZapier
 Grafana Is Not Worried About AWS CommercializationThenewstack
 When CI Meets CD: Deliver With ConfidenceThenewstack
 How We Eliminated Long-Lived CI Secrets Across 70+ ReposPulumi
 Managing dependencies - The Go Programming LanguageGo
 What is a Streaming Multiprocessor?Modal
 System UIconsCss Tricks
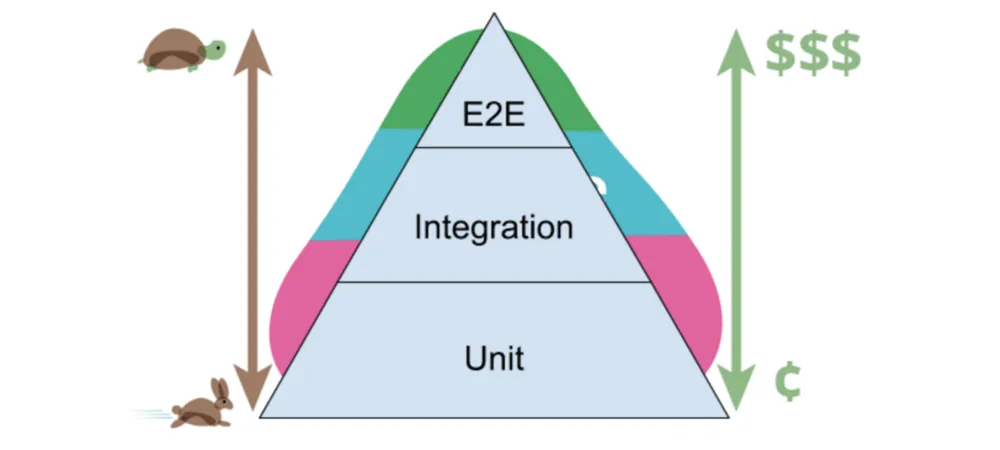 Develop, Preview, TestCss Tricks
 Some Things You Oughta Know When Working with Viewport UnitsCss Tricks
