
What we can (and can’t) learn from the latest Shadow Brokers dump
Shortly after Monday's leak, some in the digital forensics community began cross examining the IPs and domains for clues. If legitimate, the 306 domains and 352 IP addresses could offer insight into what computers a group linked to NSA may have effectively targeted between 2000 and 2010.
 Top insurer CNA disconnects systems after cyberattackcyberscoop.com
 China-based hackers used front companies to hack Uighurs, Facebook sayscyberscoop.com
 Federal advisories detail bitcoin payments to ransomware gangs, urgency of threatcyberscoop.com
 US racing to address Microsoft vulnerabilities, especially for small businessescyberscoop.com
 Energy giant Shell impacted in Accellion hackcyberscoop.com
 Thousands of Exchange servers breached prior to patching, CISA boss sayscyberscoop.com
 Cloud Security Trends & Challenges: Complete GuideCybersecurity Exchange
 Security Implementation for Responsible AI: A Practical FrameworkCybersecurity Exchange
 Breaking down common documentation mistakesMintlify
 Trained on 100,000+ Voices: Deepgram Unveils Next-Gen Speaker Diarization and Language DetectionDeepgram
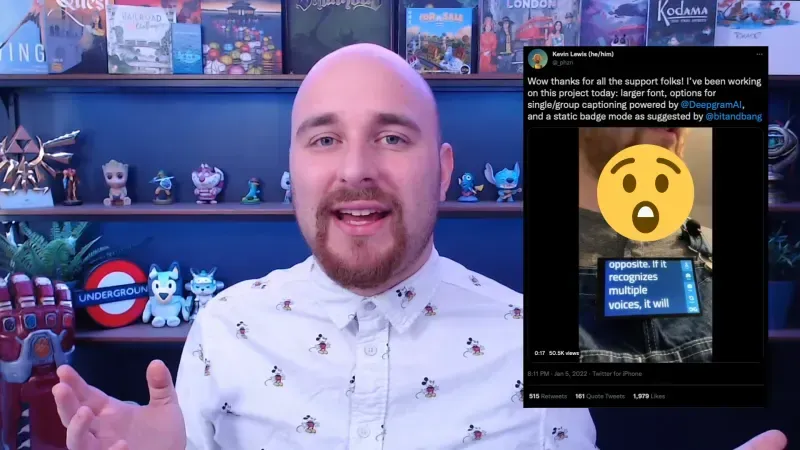 Video: Building a Live Transcription Badge With Deepgram - Deepgram Blog ⚡️Deepgram
 Playing With P5.js: Creating a Voice-Controlled Game - Deepgram Blog ⚡️Deepgram
 The Simplest Possible Neural Network, Explained - Deepgram Blog ⚡️Deepgram
 Calling Your Video Game With Your Phone: Part 1Deepgram
 Build a Presentation Coaching Application with Recall - Deepgram Blog ⚡️Deepgram
 Top 3 Use Cases for Speech-to-Text in Gaming - Deepgram Blog ⚡️Deepgram
 The Best (and Worst?) of Voice AI TechnologyDeepgram
 No Code Transcription: Simplifying Workflows with Deepgram and Make.comDeepgram
 Mind the Gap: The Chasm Between AI Fiction and Fact - Deepgram Blog ⚡️Deepgram
 Automate Audio Transcription with Zapier + DeepgramDeepgram
