
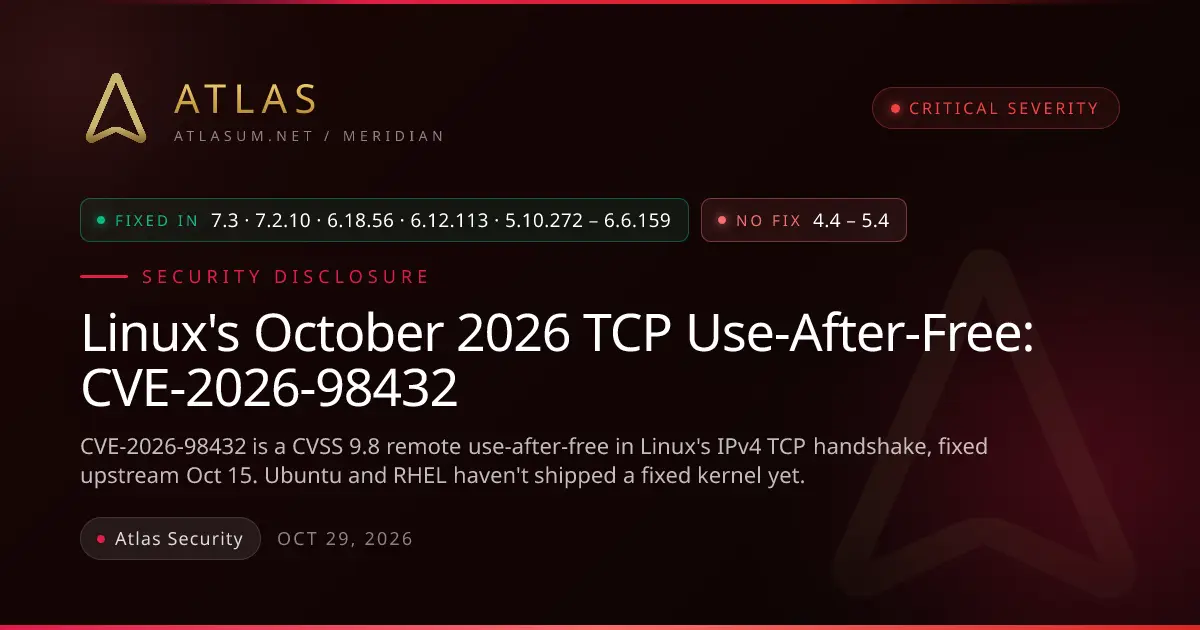
Operators should move to a kernel that carries the upstream fix for CVE-2026-98432, a use-after-free in the IPv4 TCP handshake reachable by a remote, unauthenticated peer. The upstream fix is a four-line change, but most servers run a distribution kernel, so the operative constraint is the distro tracker, not the upstream version number.
Recommended
 The AI cost of JavaScript frameworksHacker News
 AI agent swarms in Minecraft fail to build civilization, drown in bureaucracyHacker News
 Pancakes Are Delicious and Data Centers Are for Free StuffThenewstack
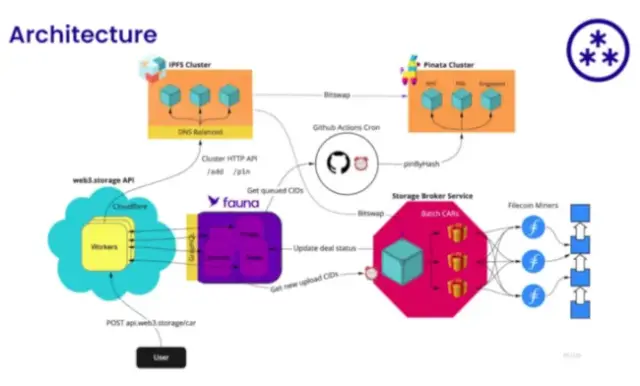 Web3.Storage: Free Decentralized Storage on FilecoinThenewstack
 4 Ways to Get Your Code Back in Shape After Black FridayThenewstack
 For Better or Worse, Richard Stallman Returns to the Free Software FoundationThenewstack
 Docs-as-code solutions for API teams: how to choose the right platform in 2026Mintlify
 10 best AI observability tools for monitoring and evaluating agents in 2026Mintlify
 Who Explains the Most? An Analysis of Educational YouTubers - Deepgram Blog ⚡️Deepgram
 Calling Your Video Game With Your Phone: Part 1Deepgram
 Build a Presentation Coaching Application with Recall - Deepgram Blog ⚡️Deepgram
 Top 3 Use Cases for Speech-to-Text in Gaming - Deepgram Blog ⚡️Deepgram
 New Spanish and Turkish Language Models and Updated General Models - Deepgram Blog ⚡️Deepgram
 Automate Audio Transcription with Zapier + DeepgramDeepgram
 Rapid `14 Q1 Growth, 23K+ Customers, 45K+ Instances, 4 Clouds (and 10 Regions)Redis
How Redis is Used in Practice | RedisRedis
A Success Story Worth Sharing: Glide.me and Redis LabsRedis
 The 8 Best HubSpot Alternatives in 2026Zapier
 Workato integrations: What's included and when to use ZapierZapier
 6 ways to use the Zapier Zoho CRM integrationZapier
