
SwampUP: DevOps Needs Guardrails, Not Gates, for Security
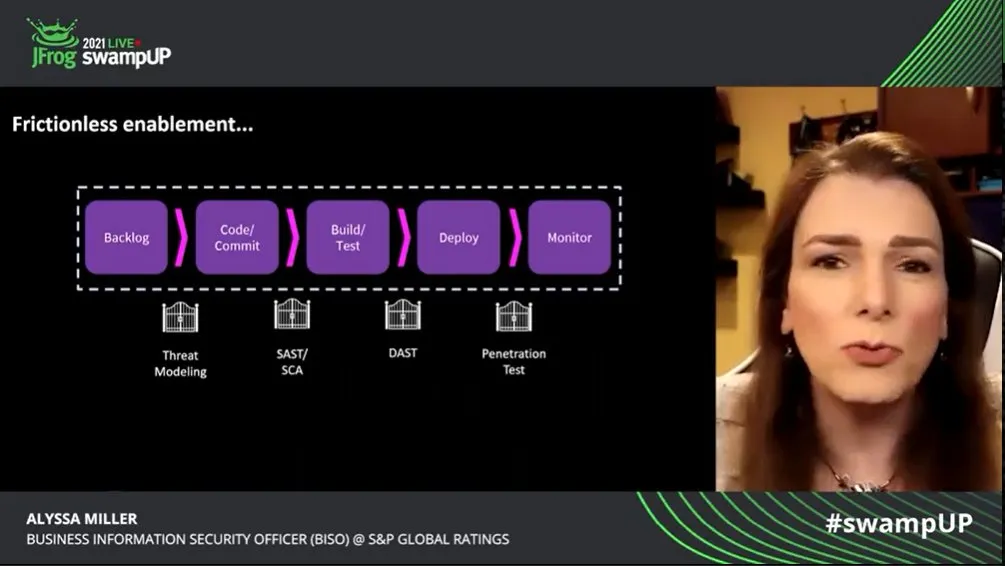
Baking security into the rapidly-iterating DevOps shops (via "shift left") continues to be a challenge, though some smart thinkers at JFrog's recent SwampUP virtual conference have a few ideas on how to make it happen.
 Refactoring Is Not Bad, Until It IsThenewstack
How Cloud Workload Protection Is Different than Application SecurityThenewstack
 Grafana Is Not Worried About AWS CommercializationThenewstack
 DevSecOps: Why Security Shouldn’t be Sacrificed for SpeedThenewstack
 Security Considerations for API-Driven Apps Deployed to CloudThenewstack
 Oso Unbundles Security AuthorizationThenewstack
 Cloud Security Trends & Challenges: Complete GuideCybersecurity Exchange
 Security Implementation for Responsible AI: A Practical FrameworkCybersecurity Exchange
 How to Conduct an AI Agent Security Audit [+ Checklist]Zapier
 Workato integrations: What's included and when to use ZapierZapier
 When CI Meets CD: Deliver With ConfidenceThenewstack
 OData or GraphQL? The Best Tech for Developing an API Is Neither or Both!Thenewstack
 Pulumi ESC and External Secrets Operator: The Perfect Solution for TodayPulumi
 Platform Engineering & DevOps Series Kickoff AnnouncementPulumi
 IaC Best Practices: Implementing RBAC and SecurityPulumi
 Inside the Go Playground - The Go Programming LanguageGo
 Summer Data Engineering RoadmapMotherduck
 Revisiting Docker Hub Policies: Prioritizing Developer ExperienceDocker
 Docker at Cloud Expo Asia: GenAI, Security, and New InnovationsDocker
 Docker Networking Drivers - Details and Use CasesDocker
