
AI vs Traditional Penetration Testing: Tooling and Outcomes
Second part of the AI vs Traditional Pentesting series, focusing this time on tools and outcomes of both approaches.
 When AI Becomes the Weak Link: Rethinking Supply Chain Securityoffsec.com
 CVE-2024-13059: Exploiting Path Traversal in AnythingLLM for Remote Code Executionoffsec.com
 CVE-2025-32433: Vulnerability in Erlang/OTP SSH Implementationoffsec.com
 CVE-2025-29927: Next.js Middleware Authorization Bypassoffsec.com
 CVE-2024-2928: MLflow Local File Inclusion via URI Fragment Manipulationoffsec.com
 CVE-2025-23211: Tandoor Recipes Jinja2 SSTI to Remote Code Executionoffsec.com
 Cloud Systems: Deploying to Amazon ECSPulumi
 Supporting Kubernetes with Faster, Easier Test EnvironmentsPulumi
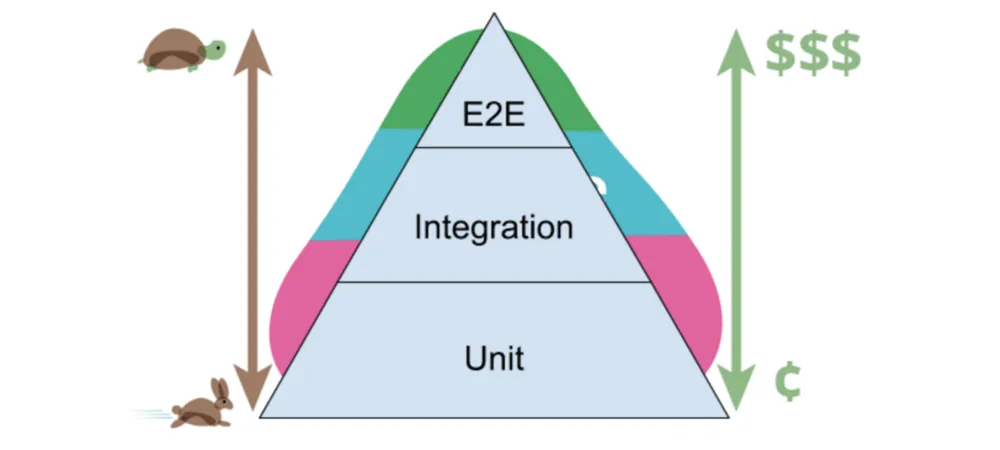 Develop, Preview, TestCss Tricks
 Announcing Python Tooling ImprovementsPulumi
 The 5 best AI search engines in 2026Zapier
 Cleaning up import paths in JS/TS packagesSocket
 5 Monitoring Characteristics SREs Must EmbraceThenewstack
 Lessons Learned from a Year of Testing the Web PlatformCss Tricks
 7 best MCP servers for Claude Code in 2026Mintlify
 Vulnerability Scanning is BrokenSocket
 Why Your SCA Tool SucksSocket
 The Problem with Transatlantic Data TransfersThenewstack
 Beyond API Security Testing: Runtime ProtectionThenewstack
 Unit Testing Cloud Deployments with .NETPulumi
