
Critical CVE in React Server Components Actively Exploited
A critical RCE flaw in React Server Components is being exploited in the wild. Learn what CVE 2025 55182 means for React and Next.js users and how Aqua helps you stay protected.
 CorePlague: Critical Vulnerabilities in Jenkins Server Lead to RCEAquasec
 Looney Tunables Vulnerability Exploited by KinsingAquasec
 Linguistic Lumberjack: Understanding CVE-2024-4323 in Fluent BitAquasec
Threat Alert: TeamTNT Pwn Campaign Against Docker and K8s EnvironmentsAquasec
Malware Forensic Analysis: Capturing What Attackers Leave BehindAquasec
 Cloud Workload Security: Aqua Shines in GigaOm's Radar ReportAquasec
 Mintlify Alternatives: What to Consider (and Why There's No True Substitute)Mintlify
 Playing With P5.js: Creating a Voice-Controlled Game - Deepgram Blog ⚡️Deepgram
 Calling Your Video Game With Your Phone: Part 1Deepgram
 How to connect Google Sheets to NotionZapier
 Announcing Restore Stacks: Recover Deleted Stacks in the Pulumi CloudPulumi
 The failed promise of Web ComponentsCss Tricks
 Server-Side React RenderingCss Tricks
 Svelte for the Experienced React DevCss Tricks
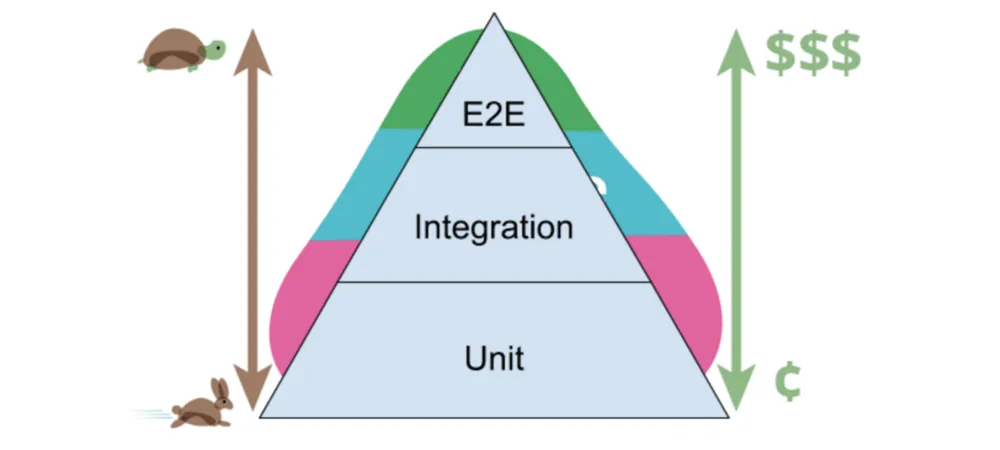 Develop, Preview, TestCss Tricks
 Jetpack Boost Handles Critical CSS For YouCss Tricks
 Building a Remote MCP Server: OAuth, Tool Design & Lessons from 4,000+ AI Queries | MotherDuckMotherduck
 The Serverless Backend for Analytics: Introducing MotherDuck’s Native Integration on VercelMotherduck
 The Anatomy of shadcn/ui ComponentsVercel
 NO_EXTERNAL_CSS_AT_IMPORTSVercel
