
CVE-2022-32223 Discovery: DLL Hijacking via npm CLI
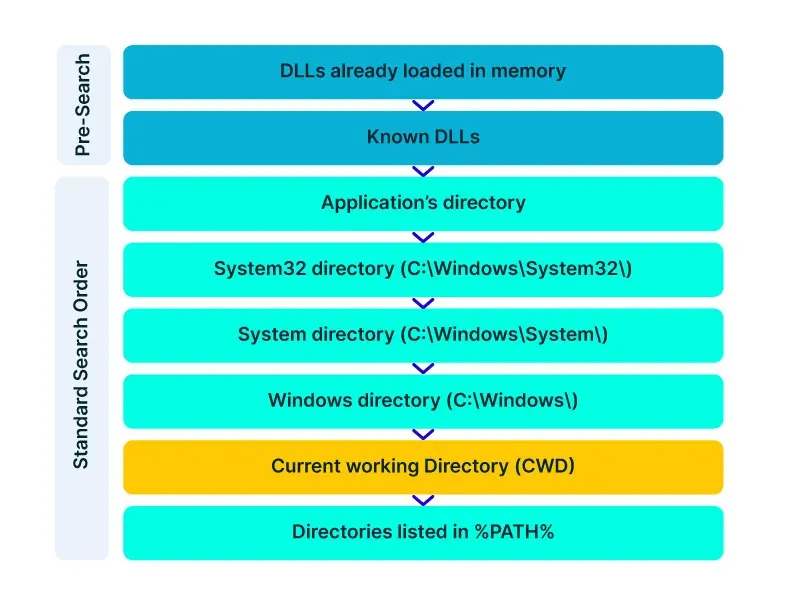
Aqua Team Nautilus recently discovered that all Node.js versions earlier than 16.16.0 (LTS) and 14.20.0 on Windows are vulnerable to dynamic link library (DLL) hijacking if OpenSSL is installed on the host.
 Threat Alert: Private npm Packages Disclosed via Timing AttacksAquasec
 Deceptive Deprecation: The Truth About npm Deprecated PackagesAquasec
 Linguistic Lumberjack: Understanding CVE-2024-4323 in Fluent BitAquasec
 New npm Flaws Let Attackers Better Target Packages for Account TakeoverAquasec
Threat Alert: TeamTNT Pwn Campaign Against Docker and K8s EnvironmentsAquasec
Malware Forensic Analysis: Capturing What Attackers Leave BehindAquasec
 Calling Your Video Game With Your Phone: Part 1Deepgram
 The Go Memory Model - The Go Programming LanguageGo
 CLI ReferenceModal
 Cerebras Systems Enables GPU-Impossible™ Long Sequence Lengths Improving Accuracy in NaturalCerebras
 Docker Desktop 4.18: Docker Scout Updates, Container File Explorer GADocker
 Best Documentation Platforms for AI Agents in 2026Mintlify
 Updated and Ongoing Supply Chain Attack Targets CrowdStrike npm PackagesSocket
 upm Launches as a Fast, Tiny Package Manager Written in TypeScriptSocket
 Happy Birthday, Shai-HuludSocket
 GlassWorm Loader Hits Open VSX via Developer Account CompromiseSocket
 Announcing OpenAPI support for the Pulumi Cloud REST APIPulumi
 This Month in the DuckDB Ecosystem: January 2026Motherduck
 Cerebras Systems and National Energy Technology Laboratory Set New Milestones for High-PerformanceCerebras
 nference Accelerates Self-Supervised Language Model Training with Cerebras CS-2 System - CerebrasCerebras
