
Patch, Ditch, Dodge, or Deal? Your Call on Vulnerabilities
Security teams are drowning in vulnerabilities. Cloud native environments can generate tens of thousands of new findings every month, even before factoring in CI/CD pipelines and third party dependencies.
 Remediate Vulnerabilities with Integrated Aqua and ServiceNow WorkflowsAquasec
 Mitigating Leaky Vessels Vulnerabilities in runc, BuildKit and MobyAquasec
CorePlague: Critical Vulnerabilities in Jenkins Server Lead to RCEAquasec
Threat Alert: TeamTNT Pwn Campaign Against Docker and K8s EnvironmentsAquasec
Malware Forensic Analysis: Capturing What Attackers Leave BehindAquasec
 Cloud Workload Security: Aqua Shines in GigaOm's Radar ReportAquasec
 Calling Your Video Game With Your Phone: Part 1Deepgram
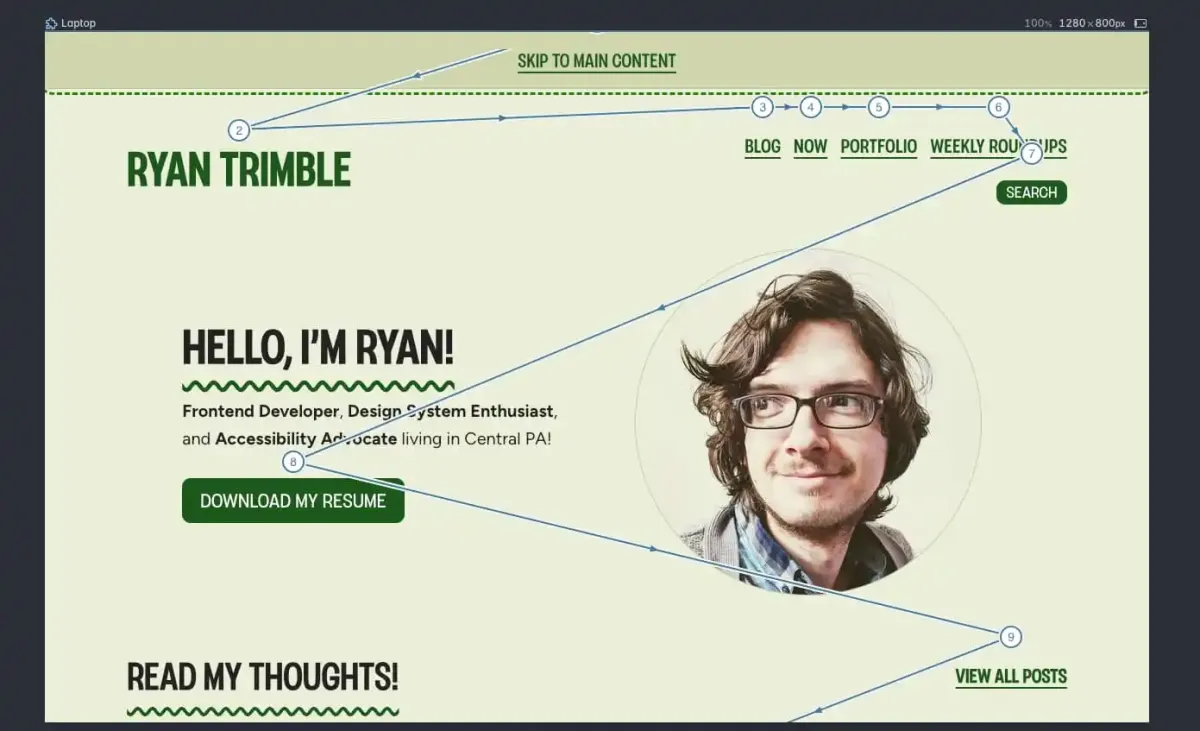 Clever Polypane Debugging Features I'm LovingCss Tricks
 Creating Color Themes With Custom Properties, HSL, and a Little calc()Css Tricks
 Cerebras Systems, Ranovus win $45 million US military deal to speed up chip connectionsCerebras
 DockerCon LIVE with theCUBE: Call for Papers is OpenDocker
 Why you should ditch spreadsheets for TablesZapier
 How to use automation to close high value dealsZapier
 Announcing Socket Certified Patches: One-Click Fixes for Vulnerable DependenciesSocket
 Last Call: Register for our next Community All Hands on March 31stDocker
 runc container breakout vulnerabilities: A technical overviewCncf
 Log Deepgram Call Summaries In SalesforceDeepgram
 Deepgram and PyTorch: The Origins of Our Foundational AI Company - Deepgram Blog ⚡️Deepgram
 White House Launches Gold Eagle Initiative to Manage Surge in AI-Discovered VulnerabilitiesSocket
 Sink or Swim: Tackling 2024's Record-Breaking Vulnerability WaveAquasec
