
Public Travis CI Logs (Still) Expose Users to Cyber Attacks
Yakir Kadkoda Ilay Goldman Assaf Morag Ofek Itach June 13, 2022 In our latest research, we at Team Nautilus found that tens of thousands of user tokens are exposed via the Travis CI API, which allows anyone to access historical clear-text logs.
 PowerHell: Active Flaws in PowerShell Gallery Expose Users to AttacksAquasec
 Real-world Cyber Attacks Targeting Data Science ToolsAquasec
 Threat Alert: Tracking Real-World Apache Log4j AttacksAquasec
 Threat Alert: Private npm Packages Disclosed via Timing AttacksAquasec
Threat Alert: TeamTNT Pwn Campaign Against Docker and K8s EnvironmentsAquasec
Malware Forensic Analysis: Capturing What Attackers Leave BehindAquasec
 A Guide to Extended Threat Detection and Response: What It Is and How to Choose the Best SolutionsCybersecurity Exchange
 How we grew Mintlify by doing things that don't scaleMintlify
 How Argo CD and OpenShift Enable GitOps for DevelopersThenewstack
 Cerebras Systems Announces Filing of Registration Statement for Proposed Initial Public OfferingCerebras
 Capturing Logs in Docker DesktopDocker
 How the world’s biggest YouTuber served millions of users on VercelVercel
 GitHub - MintlifyMintlify
 Introducing Dependency Divergence GitHub ActionSocket
 Twitch Browser Extension Exposes 30,000 Users’ OAuth Tokens to Russian Bot ServiceSocket
 737 Chrome VPN Extensions Linked to Brand Impersonation and Browser Traffic RedirectionSocket
 Be the Hero in Your Real-Life Cyber Heist ScriptThenewstack
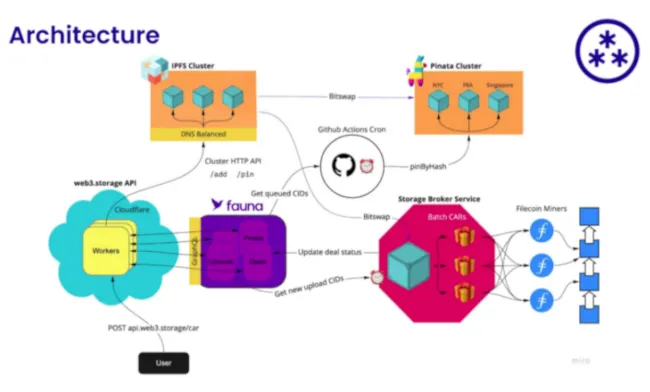 Web3.Storage: Free Decentralized Storage on FilecoinThenewstack
 Supply Chain Attacks and Cloud Native: What You Need to KnowThenewstack
 Pulumi Context API: query your infrastructure as a graphPulumi
