
Threat Alert: Maneuver Docker API for Host Takeover
A new attack vector running on-top of unsecured docker socket API was disclosed by aqua labs.
 Threat Alert: TeamTNT Pwn Campaign Against Docker and K8s EnvironmentsAquasec
 Threat Alert: Tracking Real-World Apache Log4j AttacksAquasec
 Threat Alert: Private npm Packages Disclosed via Timing AttacksAquasec
 TrailShark: Understanding AWS API and Service InteractionsAquasec
 New npm Flaws Let Attackers Better Target Packages for Account TakeoverAquasec
Malware Forensic Analysis: Capturing What Attackers Leave BehindAquasec
 A Guide to Extended Threat Detection and Response: What It Is and How to Choose the Best SolutionsCybersecurity Exchange
 Docs-as-code solutions for API teams: how to choose the right platform in 2026Mintlify
 Who Explains the Most? An Analysis of Educational YouTubers - Deepgram Blog ⚡️Deepgram
 OData or GraphQL? The Best Tech for Developing an API Is Neither or Both!Thenewstack
 Flockport: Time to Start All Over Again and Return to LXC ContainersThenewstack
 Security Considerations for API-Driven Apps Deployed to CloudThenewstack
 Introducing New Slimmer Docker ImagesPulumi
 Sidecars: A low-latency trust boundary for SandboxesModal
 Modal SDKs for JavaScript and Go (alpha)Modal
 Real-Time Computational Physics with Wafer-Scale Processing [updated]Cerebras
 Docker Captain Take 5Docker
 Docker Community All Hands RecapDocker
 Docker Desktop 4.23: Updates to Docker Init, New Configuration Integrity Check, Quick SearchDocker
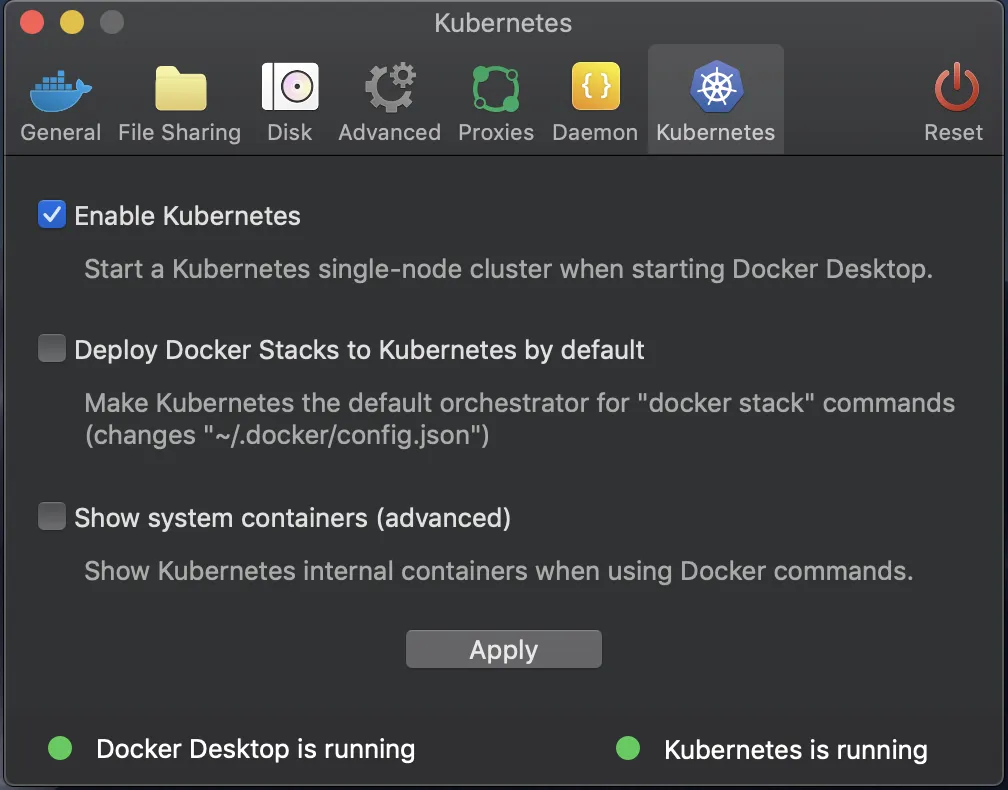 Depend on Docker for KubeflowDocker
