
Why Is Detection and Response Too Slow for Machine Speed Attacks?
TLDR: Runtime security built around detecting activity, correlating signals and then responding assumes there is enough time to act after something malicious happens.
 PowerHell: Active Flaws in PowerShell Gallery Expose Users to AttacksAquasec
 Real-world Cyber Attacks Targeting Data Science ToolsAquasec
 Threat Alert: Tracking Real-World Apache Log4j AttacksAquasec
 Threat Alert: Private npm Packages Disclosed via Timing AttacksAquasec
Threat Alert: TeamTNT Pwn Campaign Against Docker and K8s EnvironmentsAquasec
Malware Forensic Analysis: Capturing What Attackers Leave BehindAquasec
 A Guide to Extended Threat Detection and Response: What It Is and How to Choose the Best SolutionsCybersecurity Exchange
 Create assistant message - MintlifyMintlify
 Trained on 100,000+ Voices: Deepgram Unveils Next-Gen Speaker Diarization and Language DetectionDeepgram
 5 Reasons to Keep Contributing to Open-Source Projects - Deepgram Blog ⚡️Deepgram
 Data Ingestion: 6 Ways to Speed Up Your ApplicationRedis
 DevSecOps: Why Security Shouldn’t be Sacrificed for SpeedThenewstack
 Lessons Swift Designer Chris Lattner Has Learned about LeadershipThenewstack
 How to serve trillions of tokens for trillion-parameter coding agentsModal
 pg_duckdb: Splicing Duck and Elephant DNAMotherduck
 Cerebras Breaks Exascale Record for Molecular Dynamics Simulations - CerebrasCerebras
 The rise of slow personal assistantsCerebras
 Cerebras Systems, Ranovus win $45 million US military deal to speed up chip connectionsCerebras
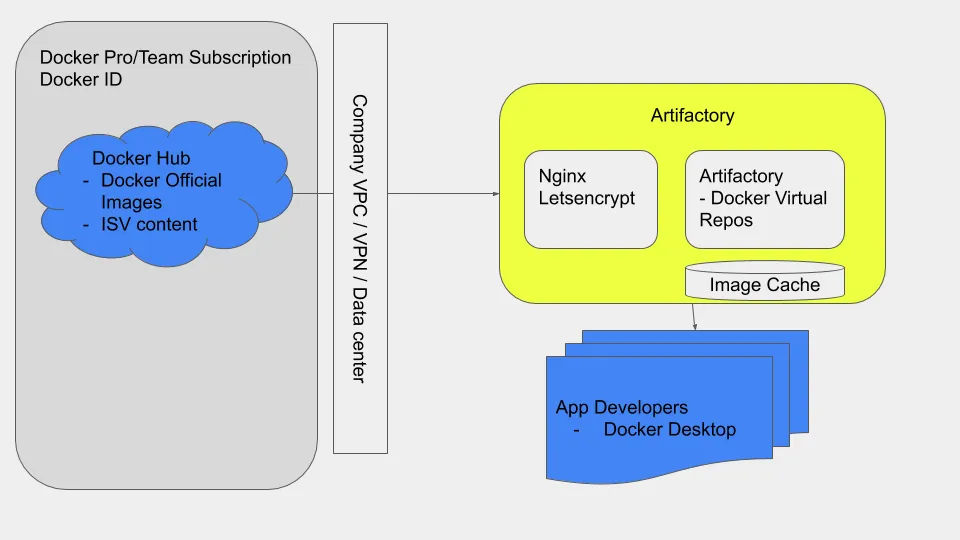 New Docker and JFrog Partnership Designed to Improve the Speed and Quality of App DevelopmentDocker
 Capturing Logs in Docker DesktopDocker
