
Accelerate incident investigations with Log Anomaly Detection
Learn how Log Anomaly Detection automatically surfaces anomalous patterns in your logs to speed up incident investigations.
 A Guide to Extended Threat Detection and Response: What It Is and How to Choose the Best SolutionsCybersecurity Exchange
 Trained on 100,000+ Voices: Deepgram Unveils Next-Gen Speaker Diarization and Language DetectionDeepgram
 Intel Unveils Next Generation Neuromorphic Computing ChipThenewstack
 Announcing the New Pulumi Partner ProgramPulumi
 Multi Face Swap Video: How to Swap Multiple Faces in a Single Video with AIHeygen
 From ASR to CSR: Why Conversation Changes EverythingDeepgram
 Using instrumentation librariesOpentelemetry
 How Sky Italia Digitizes Learning Paths to Accelerate New Product Launches by 4xSynthesia
 Policy as Code for Any Cloud ProviderPulumi
 What is OCSF and How Do You Implement It?Datadoghq
 What are Logs and How are Logs Managed?Datadoghq
What is Root Cause Analysis?Datadoghq
 Log Management & AnalyticsDatadoghq
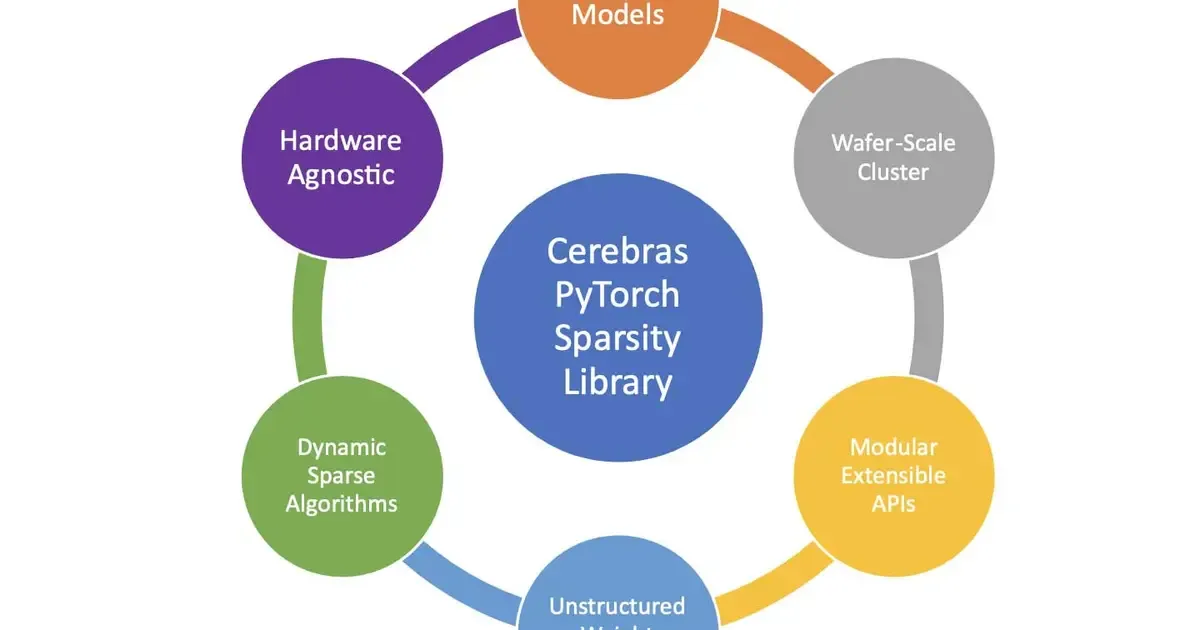 Sparsity Made EasyCerebras
