
Aqua News Unpatched Apache Tomcat servers spread Mirai botnet malware
The Nautilus researchers’ analysis established the threat actors were specifically targeting misconfigurations in the Tomcat web application manager app which allows users to manage deployed web applications.
 Lucifer DDoS botnet Malware is Targeting Apache Big-Data StackAquasec
Malware Forensic Analysis: Capturing What Attackers Leave BehindAquasec
 Cloud Workload Security: Aqua Shines in GigaOm's Radar ReportAquasec
 Aqua and HashiCorp Enable Cloud Native Security, Zero-Trust ApproachesAquasec
 Gafgyt Malware Variant Exploits GPU Power and Cloud Native EnvironmentsAquasec
 Cloud VM Security with Aqua CSPAquasec
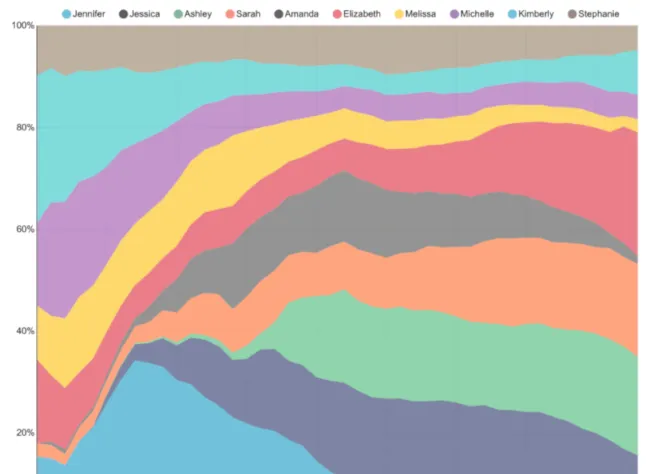 Explore and Visualize Data the Apache Superset WayThenewstack
 Neo Integrations: MCP Servers and Cloud CLIsPulumi
 Anthropic Identifies Biased Reasoning and Recklessness as Drivers of Claude’s PyPI AttackSocket
 Hands-on: Create Your First Serverless Application in Apache OpenWhiskThenewstack
 Siloscape: Windows Malware That Breaks KubernetesThenewstack
 Modal Clusters are generally availableModal
 What Is an MCP Server (Model Context Protocol Server)?Datadoghq
 Magic Containers - bunny.net DocumentationBunny
 PolinRider Spreads Through Compromised GitHub Accounts and PackagistSocket
 Socket Now Protects the Microsoft Edge Extension EcosystemSocket
 Kubernetes-Run Analytics at the Edge: Postgres, Kafka, DebeziumThenewstack
 7 best MCP servers for Claude Code in 2026Mintlify
 Socket Now Protects the Firefox Extension EcosystemSocket
 All the Apache Streaming Projects: An Exploratory GuideThenewstack
