
AWS's Predictable Bucket Names Make Accounts Easier to Crack
A key takeaway for open source projects that rely on AWS is to ensure they don't use predictable bucket names," says Yakir Kadkoda, lead security researcher with Aqua.
 TrailShark: Understanding AWS API and Service InteractionsAquasec
 Embracing the Future: AWS Customers Leverage Fargate for ECS and EKS DeploymentsAquasec
Threat Alert: TeamTNT Pwn Campaign Against Docker and K8s EnvironmentsAquasec
Malware Forensic Analysis: Capturing What Attackers Leave BehindAquasec
 Cloud Workload Security: Aqua Shines in GigaOm's Radar ReportAquasec
 Deceptive Deprecation: The Truth About npm Deprecated PackagesAquasec
 Calling Your Video Game With Your Phone: Part 1Deepgram
 No Code Transcription: Simplifying Workflows with Deepgram and Make.comDeepgram
 Re: April 23rd AWS EU-WEST-1 Service InterruptionRedis
 7 ways to use Zapier's Zendesk integrationZapier
 Grafana Is Not Worried About AWS CommercializationThenewstack
 Oso Unbundles Security AuthorizationThenewstack
 Cloud Systems: Deploying to Amazon ECSPulumi
 AWS Enterprise Container Management with PulumiPulumi
 Supporting Kubernetes with Faster, Easier Test EnvironmentsPulumi
 Neo Integrations: MCP Servers and Cloud CLIsPulumi
 Automatic cipher suite ordering in crypto/tls - The Go Programming LanguageGo
 Position Sticky and Table HeadersCss Tricks
 Scaling Organizations Should Consider Building a Website Backed by a CRM PlatformCss Tricks
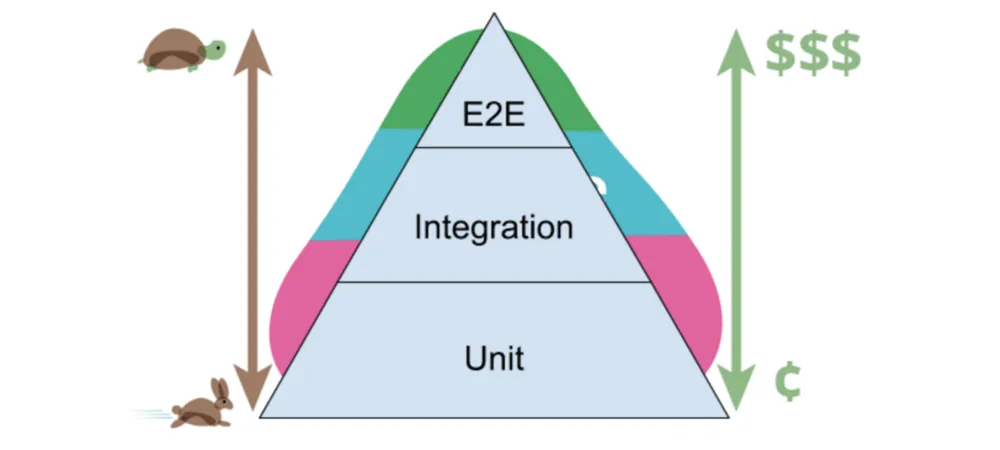 Develop, Preview, TestCss Tricks
