
Detect Exploitable Risk and Active Attacks
Aqua combines application context, runtime behavior and threat intelligence to separate real risk from noise.
 PowerHell: Active Flaws in PowerShell Gallery Expose Users to AttacksAquasec
 Real-world Cyber Attacks Targeting Data Science ToolsAquasec
 Threat Alert: Tracking Real-World Apache Log4j AttacksAquasec
 Tracee Release: Rules Detect Attackers Out-of-the-BoxAquasec
 Threat Alert: Private npm Packages Disclosed via Timing AttacksAquasec
Threat Alert: TeamTNT Pwn Campaign Against Docker and K8s EnvironmentsAquasec
 How We Eliminated Long-Lived CI Secrets Across 70+ ReposPulumi
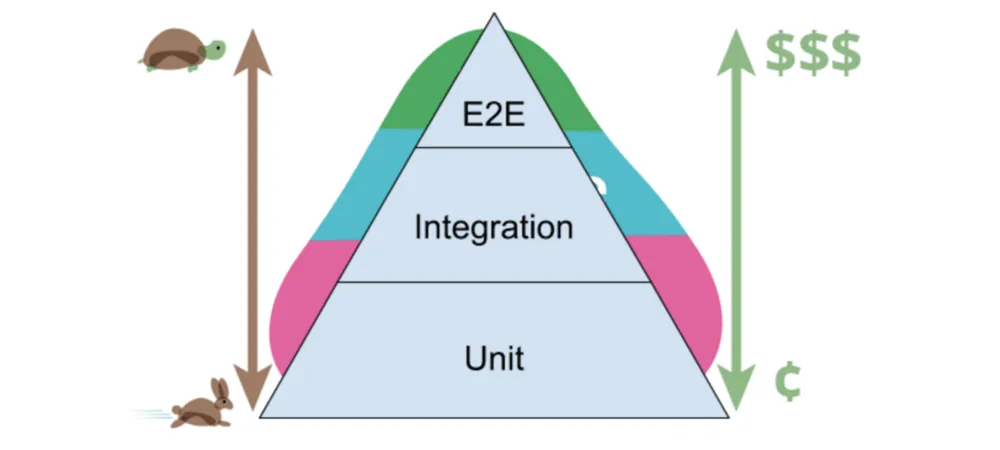 Develop, Preview, TestCss Tricks
 You can just ship agentsVercel
 Lies, damn lies, and benchmarksDeepgram
 Detect Non-Inclusive Language with Retext and Node.js - Deepgram Blog ⚡️Deepgram
 Announcing Socket Certified Patches: One-Click Fixes for Vulnerable DependenciesSocket
 Supply Chain Attacks and Cloud Native: What You Need to KnowThenewstack
 Webinar: Migrate from Legacy Platforms to Datadog with AeginDatadoghq
 Understanding CSRF attacksVercel
 Third-Party Risk Management (TPRM): A Complete GuideZapier
 AI governance: What it is + why it's importantZapier
 Popular npm Packages in the keyv and Cacheable Namespaces Compromised in Active Supply Chain AttackSocket
 Socket Now Protects the Microsoft Edge Extension EcosystemSocket
 Protecting Against CDN Cache PoisoningBunny
